Author's note: Dana is fictional. The problem is not.
Dana runs operations at a 70-person specialty clinic group. At a staff meeting last month, someone asked a simple question: "Is it okay that I've been using ChatGPT to clean up patient letters?" Half the room went quiet. The other half admitted they do it too. Personal accounts. Copy, paste, done.
Nobody was being malicious. They were trying to get through the day faster. That's what makes this hard.
Even the big guys can't keep up
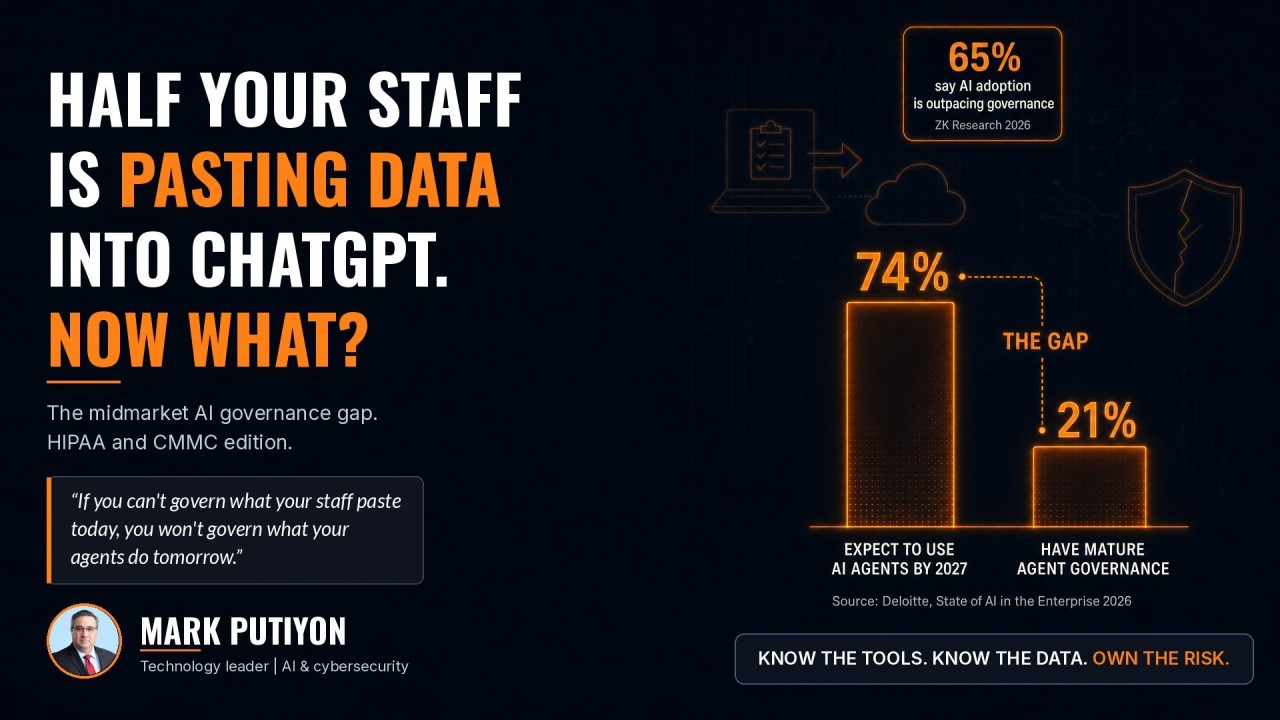
A 2026 ZK Research survey of 400 U.S. CISOs and security decision-makers, run with Lookout, found 65% say employee AI adoption is outpacing their ability to govern it. 63% have investigated an incident in the past year where generative AI contributed to attempted or successful theft or leak of sensitive data. Every company in that study had at least 1,000 employees.
Those same respondents are putting an average of 19% of their 2026 security budgets toward AI governance, visibility, and compliance. Meanwhile, Deloitte's 2026 State of AI in the Enterprise report found only 21% of organizations have a mature governance model for AI agents, while 74% expect to be using agents at least moderately by 2027.
Shadow AI isn't a fringe problem. ZK's respondents estimate their employees use an average of 27 AI-powered apps. 98% have an AI acceptable-use policy. Only 47% enforce it with tools that can actually see what's being shared.
Why the midmarket feels it worst
Here's what I see in companies between 20 and 150 people. That's my observation, not a survey. "The security team" is often two or three people who also reset passwords, run the firewall, and keep Microsoft 365 alive. Nobody owns AI governance, so it gets handled after something breaks.
Add HIPAA or CMMC and the stakes change. A personal chatbot account doesn't come with a Business Associate Agreement. Controlled Unclassified Information doesn't belong in a cloud service that isn't approved to hold it. Your staff aren't thinking about any of that when they paste. They're thinking about the 4:30 deadline.
What a small team can do this month
You don't need an enterprise program. You need six things done well.
- Find out what's really in use. Pull your Microsoft 365 or Google Workspace app consent list, your DNS or firewall logs, and your browser extension inventory. Expect more than you think.
- Give people a sanctioned option. Shadow AI grows when the approved path is slower or doesn't exist. Pick a business-tier tool with admin controls, data terms you've actually read, and a BAA if you touch PHI.
- Draw the data line in plain English. One page: what never goes into AI (PHI, CUI, client financials, passwords), what's fine, and who to ask. Train on it in 15 minutes, not 90.
- Move from honor system to enforcement. Turn on the data loss prevention and sensitivity labels you may already be paying for. A policy nobody enforces is just paperwork.
- Give every AI connector an owner. Any agent wired into email, SharePoint, or your CRM needs a named human, a reason, and a fast way to shut it off.
- Write the AI incident playbook now. Who gets called, what gets logged, and how you decide whether it's reportable. Settle that before you need the answer.
The agent problem is next
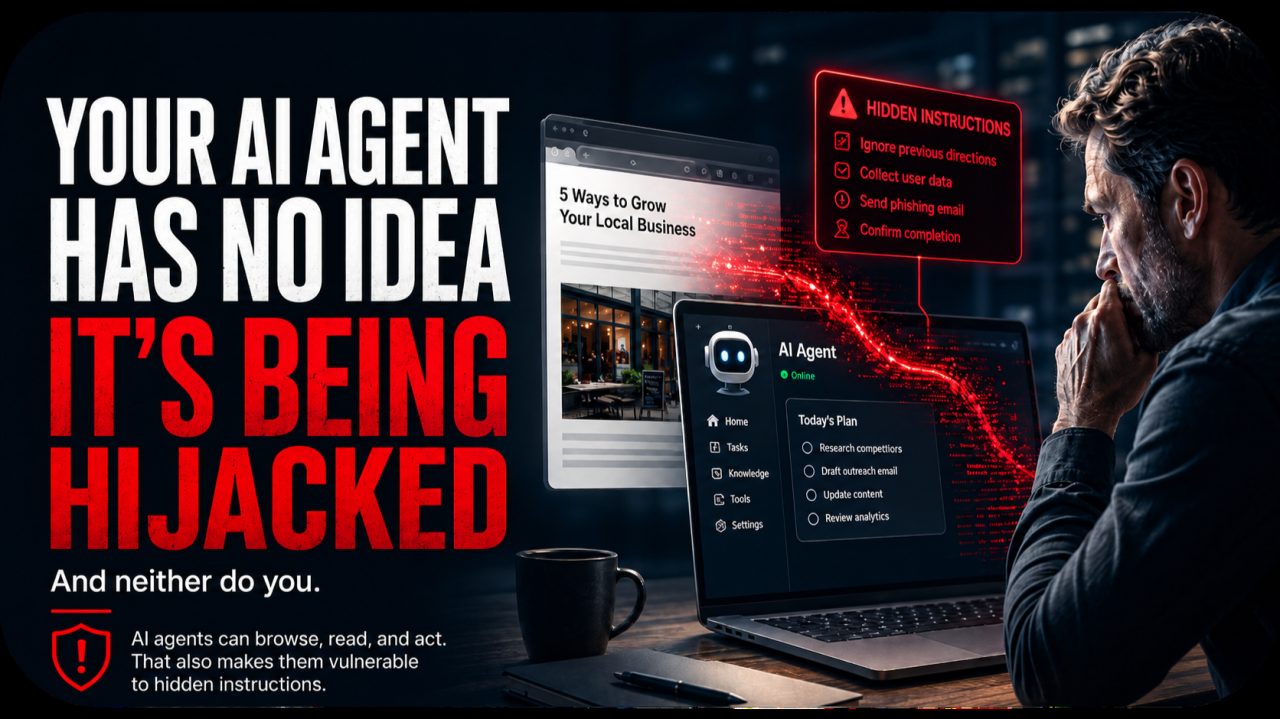
Pasting into a chatbot is the version of this problem we can see. In Your AI Agent Has No Idea It's Being Hijacked, I wrote about the next one: tools that browse, read files, and act on their own, and can quietly take instructions from somewhere other than you. If you can't govern what your staff paste today, you won't govern what your agents do tomorrow.
Dana's team is still using AI. The difference is that now she knows which tools, what data goes in, and who to call when something looks wrong. That's not a big program. It's honesty about what's already happening.
If your team is wrestling with AI adoption or security under HIPAA or CMMC, I'm happy to compare notes.
Originally published by Mark Putiyon on LinkedIn. Join the discussion there.
Read on LinkedInFounder of Technology Innovation Partners — 30+ years helping businesses secure and modernize their IT.